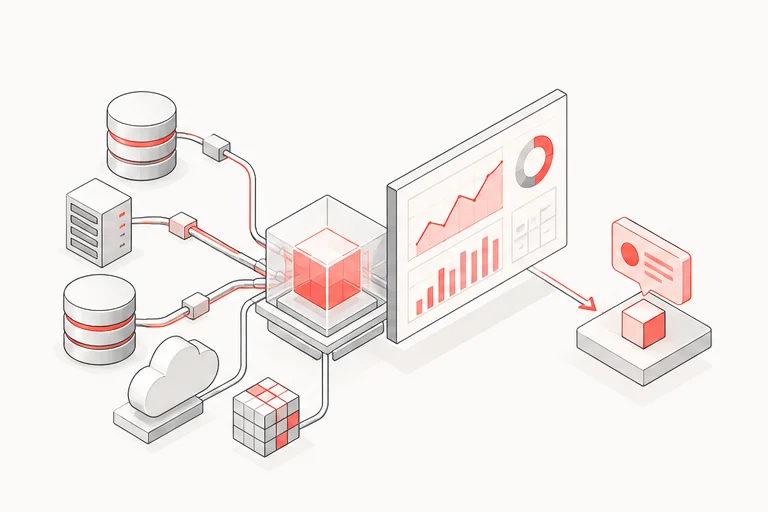
Zenveus helps teams design, secure, deploy, observe, and control AWS environments so releases are safer, incidents are easier to diagnose, and cloud spend is less mysterious.
AWS DevOps at Zenveus combines infrastructure design, deployment automation, monitoring, security controls, and operational documentation for AWS-hosted products. The goal is a cloud environment your team can understand and run, not a pile of console settings.
Technical Forensic Call (24–48h)
Architecture Blueprint & Scope
System Design + Security Hardening
AI-Accelerated Sprints + Weekly Demos
Production Launch + Scale Readiness
Zenveus commonly works with IAM, VPC, ECS, Lambda, RDS, S3, CloudFront, Route 53, CloudWatch, Secrets Manager, queues, and Terraform. The service mix depends on reliability, compliance, traffic, and cost requirements.

Turns natural-language questions into live dashboards in under 60 seconds and deploys inside the customer's AWS accou…
Read the case study →
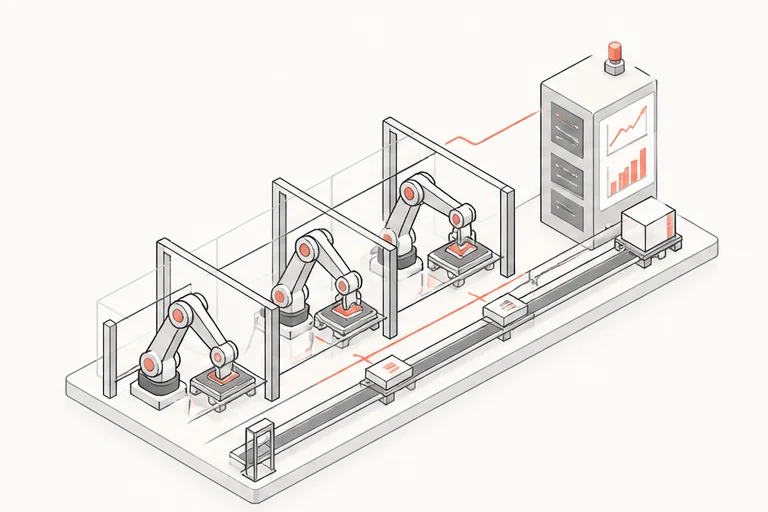
Moved factory rollouts toward repeatable deployments with clearer UX and a stronger production cloud backbone.
Read the case study →
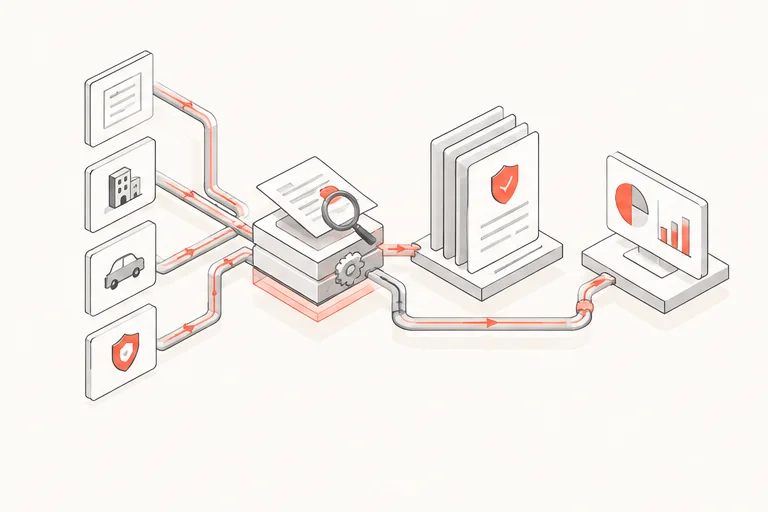
Reduced onboarding friction, minimized repetitive form entry, sped up internal evaluation, centralized broker workflo…
Read the case study →
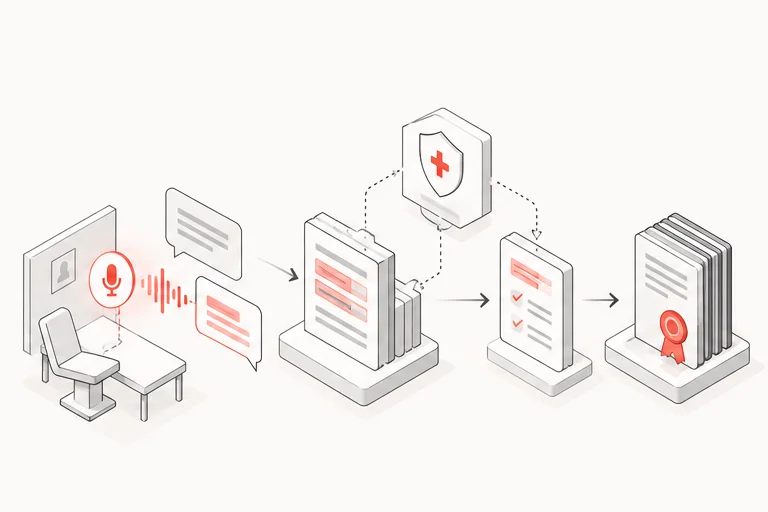
Reduced manual note writing and duplication, improved documentation consistency, strengthened compliance readiness, a…
Read the case study →
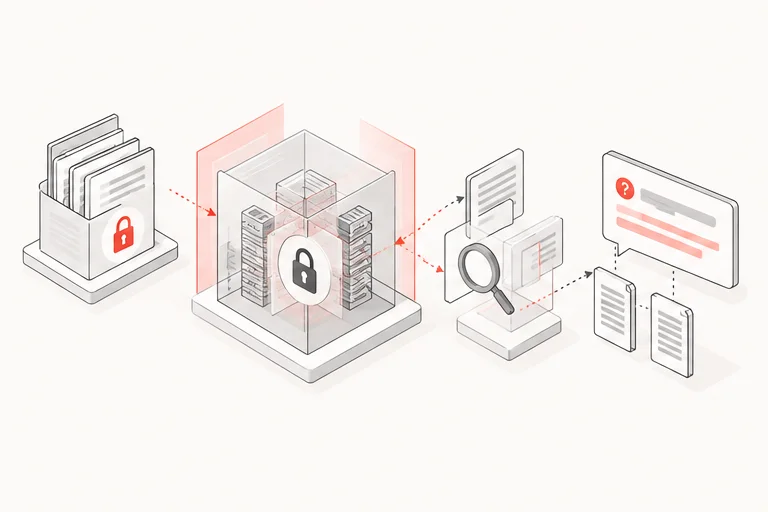
Turned uploaded legal documents into private, searchable conversational knowledge while preserving account-level sepa…
Read the case study →
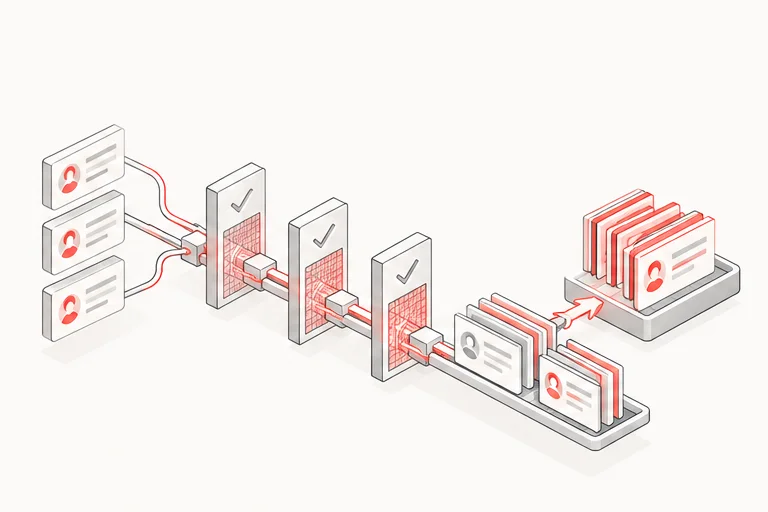
Scaled from 30-50 to 80+ leads/day, cut invalid records reaching AI to 0%, detected failures in under 30 seconds, and…
Read the case study →Yes. Zenveus can audit and improve an existing AWS environment with appropriate access and change controls.
Yes. Handover documentation and operating notes are part of the engagement when the client team will own the environment.
AWS DevOps at Zenveus combines infrastructure design, deployment automation, monitoring, security controls, and operational documentation for AWS-hosted products. The goal is a cloud environment your team can understand and run, not a pile of console settings.
Zenveus commonly works with IAM, VPC, ECS, Lambda, RDS, S3, CloudFront, Route 53, CloudWatch, Secrets Manager, queues, and Terraform. The service mix depends on reliability, compliance, traffic, and cost requirements.
Zenveus builds CI/CD pipelines, environment separation, secrets handling, rollback paths, migration discipline, and release checks. That reduces risky manual deploys and makes production changes easier to audit.
Zenveus reviews IAM scope, network boundaries, encryption, backups, logging, exposed services, secret storage, and dependency risk. Security is handled as engineering practice rather than a final checklist.
We use optional cookies for analytics and marketing. You can accept or reject them.